For decades, enterprise security has been built around a simple question: who is this user, and what should they be allowed to do? The rapid spread of artificial-intelligence agents is forcing companies to ask that question about something that is not a person at all.
As AI agents gain access to enterprise data, systems and tools, they are emerging as a new class of active identity requiring specialised permissions, monitoring and governance, according to an analysis published by Crunchbase News on September 23 by guest contributor Itay Sagie, a strategic adviser to technology companies and investors specialising in strategy, growth and mergers and acquisitions.
Sagie’s piece maps the emerging mergers-and-acquisitions landscape for AI agent security — a sign that investors and strategic buyers increasingly see this as a distinct and valuable market rather than a niche feature of existing products.
Why agents are different
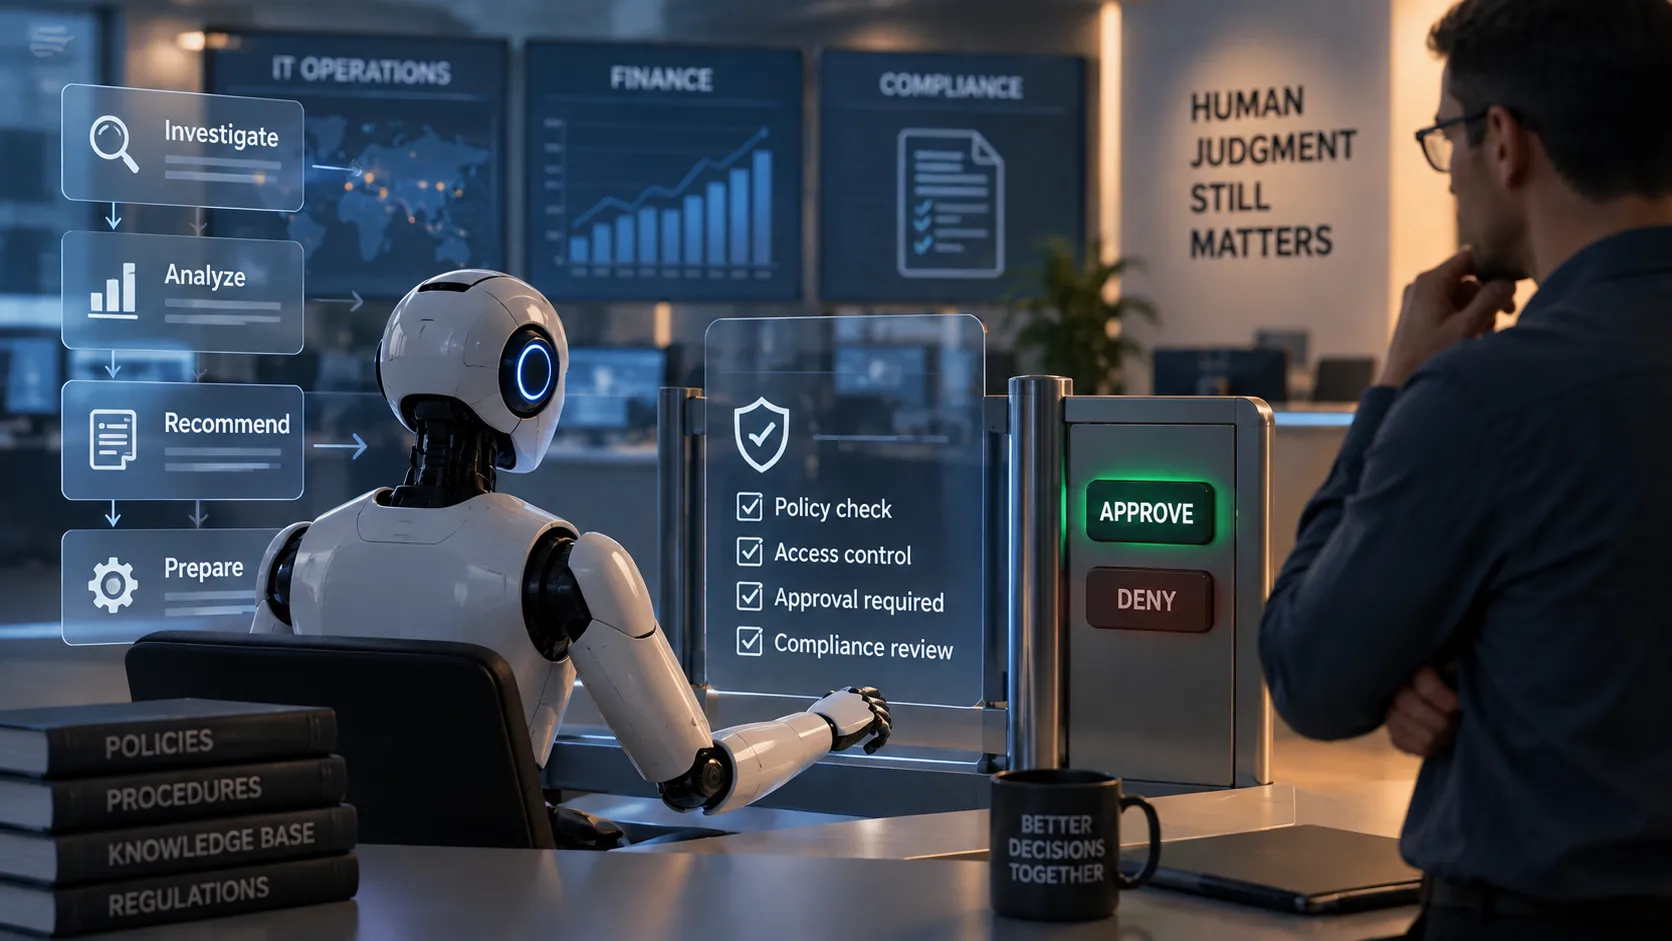
AI agents differ from traditional software in important ways. A conventional application follows predetermined logic. An agent can interpret goals, plan steps and take actions across multiple systems — reading email, querying databases, calling application programming interfaces and triggering workflows.
To do that, agents need credentials and permissions. They log into systems, access sensitive data and execute transactions, often on behalf of a human user or a business process. In security terms, that makes them identities: entities with access rights that must be authenticated, authorised, monitored and, when necessary, revoked.
The challenge is that most identity systems were designed for humans and, more recently, for relatively static machine identities such as service accounts. Agents behave differently. They may be created and retired quickly, act across many systems in rapid succession and change behaviour depending on the instructions and data they receive.
The adoption gap
Industry surveys suggest that adoption has outpaced governance. Security Boulevard reported this month that 91% of organisations use AI agents, but only 10% have a developed strategy for non-human identities. The same report cited a 2026 Dark Reading poll in which 48% of security professionals ranked agentic AI as the year’s top attack vector.
Okta has reported that 81% of chief information security officers worry about excessive AI access, while only 31% feel fully aligned with their boards on acceptable AI risk, according to Security Boulevard.
That gap creates risk. An agent with excessive permissions could be manipulated through malicious instructions hidden in the data it processes, a technique often described as prompt injection. A compromised agent could exfiltrate data, alter records or initiate transactions at machine speed, potentially before a human notices anything is wrong.
Auditability is another concern. If logs cannot distinguish between actions taken by an agent and actions taken by the human it represents, investigating incidents and assigning accountability becomes far harder.
Security vendors race to respond
The largest cybersecurity companies have moved quickly to address the problem. CrowdStrike introduced its Agentic Identity Provider on September 2, 2026, positioning its identity-security platform as the control plane for what it calls the agentic enterprise. The product is designed to establish every agent as a trusted identity, grant only the access needed for as long as needed and tie every action back to the human or system behind it, according to the company.